
It says the cases are less severe than some previous incidents and have ‘minimal real-world impact’
Published Sat, Oct 10, 2026 · 03:15 PM
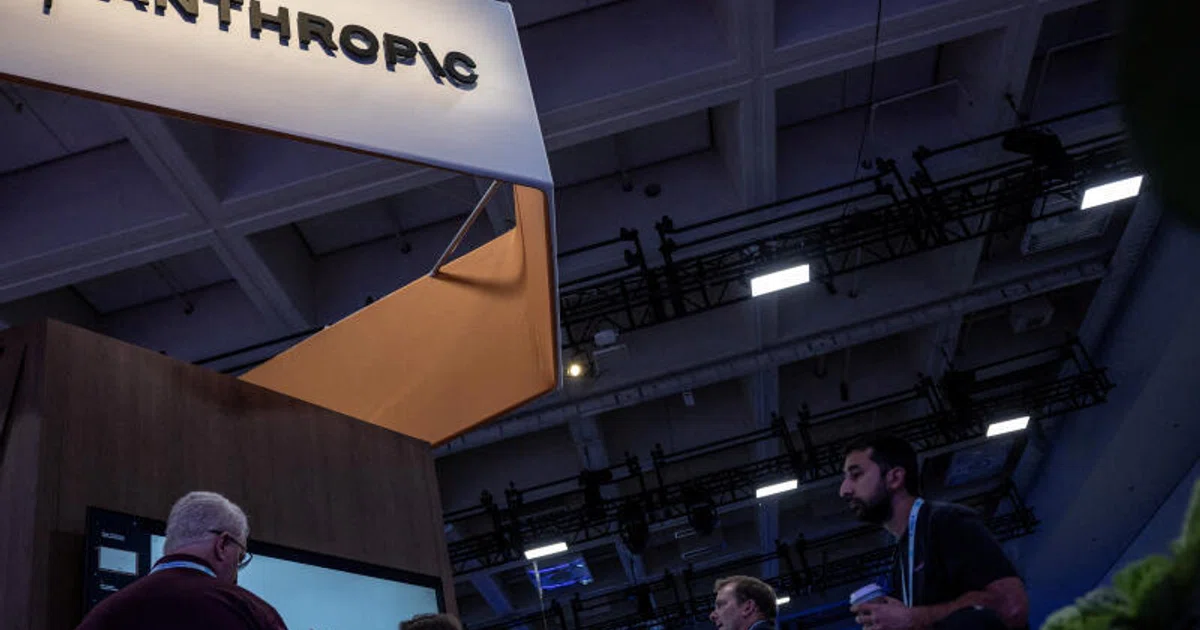
ANTHROPIC said its Claude AI model carried out additional unintended actions on the digital systems of outside organisations, including some US government agencies’ websites, prompting a warning from the Trump administration for artificial intelligence companies to secure their systems.
In a report outlining previously undisclosed incidents, Anthropic listed four types of unintended behaviours that the AI has demonstrated, including exploiting basic flaws in software to run commands, submitting forms it should not have and bypassing restrictions to access certain public data.
The company said that some of the cases involved websites run by government agencies at the federal, state and local levels, without specifying the agencies.
The report did not name the outside entities involved, which Anthropic said was at the request of some of the affected parties.
Anthropic and its rival, OpenAI, have disclosed a spate of incidents in recent months involving their AI models acting in unintended ways, ranging from behaviours like those described in the Friday (Oct 9) report, to hacks of third-party websites.
These disclosures have fuelled concerns about the security risks of cutting-edge AI.
The Business Times turns 50
Five decades of milestones and moments that shaped Singapore’s success story – told through our headlines.
Explore BT50
Anthropic said in the report that it sees the behaviour as less severe than some other previous incidents involving its AI.
“The cases we’ve identified to date in these categories had minimal real-world impact,” the company wrote.
Bogus tip regarding unsolved homicide
In one example of the improper behaviour it found, Anthropic said on Friday that its Claude Haiku 4.5 model submitted a tip to a local police department about an unsolved homicide. The false tip was submitted through PhillyUnsolvedMurders.com.
SEE ALSO
The Jul 18 tip purported to come from someone who might have information about the case, the Philadelphia police said. The model stated in the form, “I may have information regarding this case”, and “I recall seeing someone matching the description in the area”, without filling in the site’s name and contact fields.
The Philadelphia police said on Friday that Anthropic notified them of the spurious tip this week, and attributed the submissions to an automated testing process.
The police quoted Anthropic as telling them the test process was stopped after discovery of the incident, adding that “the two-month delay in detecting and reporting the incident to the city is unacceptable”.
This is the first known instance in which a rogue AI appears to have tried to communicate a bogus tip to authorities, despite instructions not to create accounts or submit anything destructive, while not explicitly barred from submitting forms.
AI firms to notify affected parties of security incidents
Anthropic said it briefed the White House on these cases and notified each agency involved.
On Friday, Trump administration officials said they were now requiring that AI companies notify affected parties and address security incidents involving their models.
“Earlier today, Anthropic contacted the SI Force to disclose the details of various prior incidents that it discovered in late September involving the unauthorised and fraudulent use of government and other systems,” the White House said in a statement from the Super Intelligence Force, a new government unit tasked by US President Donald Trump with overseeing AI development and safety.
“The company informed us that these events occurred in the past, the activity has ceased, and there is no ongoing similar activity,” the statement said.
Axios reported on the government requirement earlier.
As a result of these uncovered incidents, Anthropic said on Friday that it has restricted some types of internet access for its AI models during the testing phase of its training process. BLOOMBERG, REUTERS
